Wednesday, April 26, 2017
Offensive Security has updated the Kali Linux images with new features and changes. Termed Kali Linux 2017.1, this release comes with su...
Offensive Security has updated the Kali Linux images with new features and changes. Termed Kali Linux 2017.1, this release comes with support for wireless injection attacks to 802.11ac and Nvidia CUDA GPU. You can simply update your existing installation by running few commands if you don’t wish to download the updated images from Kali repos.
Friday, April 22, 2016
Foreword As a pentester, I love server-side vulnerabilities more than client-side ones. Why? Because it’s way much ...
|

Foreword
As a pentester, I love
server-side vulnerabilities more than client-side ones. Why? Because it’s way
much cooler to take over the server directly and gain system SHELL
privileges. <( ̄︶ ̄)>
Of course, both vulnerabilities
from the server-side and the client-side are indispensable in a perfect
penetration test. Sometimes, in order to take over the server more elegantly,
it also need some client-side vulnerabilities to do the trick. But speaking
of finding vulnerabilities, I prefer to find server-side vulnerabilities
first.
With the growing popularity
of Facebook around the world, I’ve always been interested in testing the
security of Facebook. Luckily, in 2012, Facebook launched the Bug Bounty Program, which even
motivated me to give it a shot.
|
Tuesday, September 24, 2013
It is time to make some attacks which like ddos but from only one PC :D DecFlooder-v1.00 Hack Tools easy to use as you see from the p...
It is time to make some attacks which like ddos but from only one PC :D
DecFlooder-v1.00 Hack Tools
easy to use as you see from the picture
- just select your connection speed
- add victim URL
- then pust the Enjoy Button :D ( FLOOD !!!)
Download Link:
Tuesday, August 02, 2011
Below are the inside details of Florida voting systems. If the United States government can't even keep their ballot systems secure, why...
Below are the inside details of Florida voting systems. If the United States government can't even keep their ballot systems secure, why trust them at all? Everyone knows voting is rigged, but if you don't here you go.
Twitter - @AnonymousWiki
Monday, May 02, 2011
An amusing attack was demonstrated in the course of the last penetration testing. It is a good example of practical application of Cross-Si...
An amusing attack was demonstrated in the course of the last penetration testing. It is a good example of practical application of Cross-Site Scripting. We had the following situation:
- User segment with an attacker (me) operating from it;
- Technological network with strictly restricted outgoing traffic;
- A web application in the technological network that is vulnerable to Remote File Including (RFI);
- A web application in the technological network that is vulnerable to SQL Injection.
Monday, May 02, 2011
A method that I discovered today in MySQL documentation struck me with its simplicity and the fact that I haven’t noticed it before. Let me ...
A method that I discovered today in MySQL documentation struck me with its simplicity and the fact that I haven’t noticed it before. Let me describe this method of bypassing WAF.
MySQL servers allow one to use comments of the following type:
/*!sql-code*/ and /*!12345sql-code*/
As can be noticed, SQL code will be executed from the comment in both cases! The latter construction means that "sql-code" should be executed only if the DBMS version is later than the given value.
Some WAFs skip comments during signature search. Among such WAFs, there is the latest stable assembly of Mod_Security (v. 2.5.9).
Here is a simple example:
Wednesday, April 13, 2011
A few months ago, I released a new version of both SmartSniff and SniffPass with support for using them with Microsoft Network Monitor 3.x...
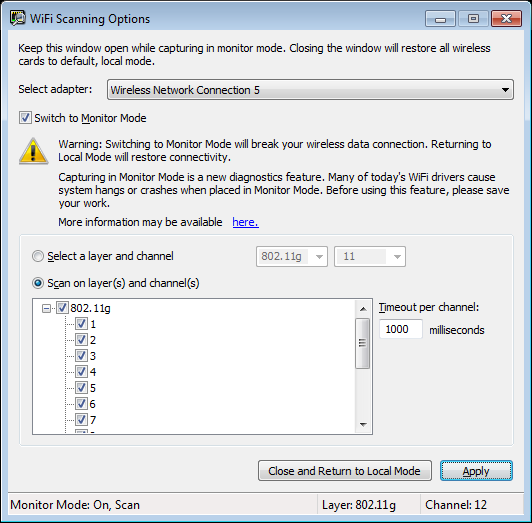
In the release details, I also specified that 'Wifi Monitor Mode' button was added for using 'Monitor Mode' under Windows Vista/7/2008, but without giving extensive explanation about how to use this feature. So in this blog post, I'll add more details about this 'Wifi Monitor Mode' and how to use it on SmartSniff and SniffPass.
When a wireless network card enters into a 'Monitor Mode', it listens to specific channel that you choose and captures all the packets that are sent by wireless networks on your area in the specific channel that you selected. If the wireless network that sent the packet is unsecured, SmartSniff and SniffPass will be able to show you the packets data.
Before I start to explain you how to use this mode, here's the system requirements for using 'Monitor Mode':
Thursday, April 07, 2011
DRIL (Domain Reverse IP Lookup) Tool is a Reverse Domain Tool that will really be useful for penetration testers to find out the domain na...
DRIL (Domain Reverse IP Lookup) Tool is a Reverse Domain Tool that will really be useful for penetration testers to find out the domain names which are listed in the the target host, DRIL is a GUI, JAVA based application which uses a
Bing API key.
DRIL has a simple user friendly interface which will be helpful for penetration tester to do their work fast without a mess, this is only tested on Linux but as it is JAVA it should work on Windows too.
There are various other tools which carry out similar tasks, especially utilizing the Bing API.
You can download DRIL here:
Thursday, March 24, 2011
"The vulnerability that I want to share first, Is a critical vulnerability in Blogger (Google Service), That vulnerability could be us...
"The vulnerability that I want to share first, Is a critical vulnerability in Blogger (Google Service),
That vulnerability could be used by an attacker to get administrator privilege over any blogger account (Permission Issue),Yes I know it sound kind of crazy but it's true :),
Here are the details regarding the issue in Blogger service,
I found a HTTP Parameter Pollution vulnerability in Blogger that allow an attacker to add himself as an administrator on the victim's blogger account,"
Wednesday, March 23, 2011
After a very successfull release of Sql Poizon v1.0, The Exploit Scanner Tool, I am hereby introducing you with the new release which is m...
After a very successfull release of Sql Poizon v1.0, The Exploit Scanner Tool, I am hereby introducing you with the new release which is more handy. It has new features as well as bug fixes from the older release. Please take a look for it below:
Sunday, March 20, 2011
One of my blog readers asked me "How can i use trial version software's forever" .Instead of answering him i taught i can wr...
One of my blog readers asked me "How can i use trial version software's forever" .Instead of answering him i taught i can write a tutorial on How to use trial version software's for Ever
Concept :-
When you install a software for the first time it makes an entry into the Windows Registry with details such as Installed Date and Time, installed path etc.After installation every time you run the software it compares the current system date and time with the installed date and time.So with this it can make out whether the trial period is expired or not. So if we make software think that the trial period is not over we can use the software for ever
Sunday, March 13, 2011
Recently HotFile.com got itself in big legal trouble which forced them to start (really) deleting "copyrighted" material, and ...
Recently HotFile.com got itself in big legal trouble which forced them to start (really) deleting "copyrighted" material, and banning uploaders who kept "infringing copyright" by continuing to upload their files to HotFile. This ended up in starting a whole new compitition in the Cyberlocker/Filehosting market. New hosts such as FileServe, and FileSonic now own the greatest part of the market.

Anyway, enough blah bla. Lets get to the point!
Some uploaders still dare to upload files to HotFile and on average those files get deleted withing 30 minutes, but do they really delete files? Aperently not, and we found out how to download "deleted" files. this trick is superb easy and you need now knowledge aside how to use a browser!Let me show you: Here we have a link which is "deleted"
http://hotfile.com/dl/109695738/8cec3a0/...e.avi.html
See the usual "File deleted bla bla bla" message.
Now the trick. You simply have to place new before the URL and then it will work again! :woohoo:
http://new.hotfile.com/dl/109695738/8cec3a0/national.geographic.kkk.inside.american.terror.hdtv.xvid-diverge.avi.html
I've sucsessfully tested this trick with both free & premium user!
Yeah, that simple! Enjoy while it lasts!
It looks like a bug, so I expect it to be "fixed" soon
Friday, March 04, 2011
Hakin9 is a free, online, monthly publication on IT Security. The magazine is published in English and is available in the Internet a...
Hakin9 is a free, online, monthly publication on IT Security. The magazine is published in English and is available in the Internet as a FREE download. It is a source of advanced, practical guidelines regarding the latest hacking methods as well as the ways of securing systems, networks and applications.
Wednesday, February 16, 2011
Gray Hat Hacking The Ethical Hackers Handbook, 3rd Edition http://www.amazon.com/Gray-Hacking-Ethical-Hackers-Handbook/dp/0071742557/ * ...

Gray Hat Hacking The Ethical Hackers Handbook, 3rd Edition
http://www.amazon.com/Gray-Hacking-Ethical-Hackers-Handbook/dp/0071742557/
* Develop and launch exploits using BackTrack and Metasploit
* Employ physical, social engineering, and insider attack techniques
* Build Perl, Python, and Ruby scripts that initiate stack buffer overflows
* Understand and prevent malicious content in Adobe, Office, and multimedia files
* Detect and block client-side, Web server, VoIP, and SCADA attacks
* Reverse engineer, fuzz, and decompile Windows and Linux software
* Develop SQL injection, cross-site scripting, and forgery exploits
* Trap malware and rootkits using honeypots and SandBoxes